Under audit now. Targeted for January 2027.
An outside auditor is actively reviewing our controls across SOC 1, SOC 2, and ISO 27001. The control documentation already exists, and your security team is welcome to review it while the audit runs.
Your security team can review the current documentation before a pilot begins.
Three frameworks, one timeline.
All three are running concurrently with the same external assessor. Here is what each one covers and exactly where it is, described the way we would describe it to your auditor.
The financial and operational controls behind the platform.
- Status under independent audit, targeted January 2027
- Why it matters where our processing affects your financial reporting, your auditors will ask for this one
Security, availability, and confidentiality controls.
- Status under independent audit, targeted January 2027
- Why it matters the report most retail security teams ask for first when assessing a SaaS vendor
The international standard for information security management.
- Status running in parallel with the SOC work, targeted January 2027
- Why it matters usually the requirement for European and Middle Eastern procurement
Until each report is issued, we describe these as under audit rather than achieved. When each one completes, what we will send you is the report itself.
Controls do not wait for the certificate.
The audit confirms what is already in place. These are the safeguards operating now, independent of where the reports have got to.
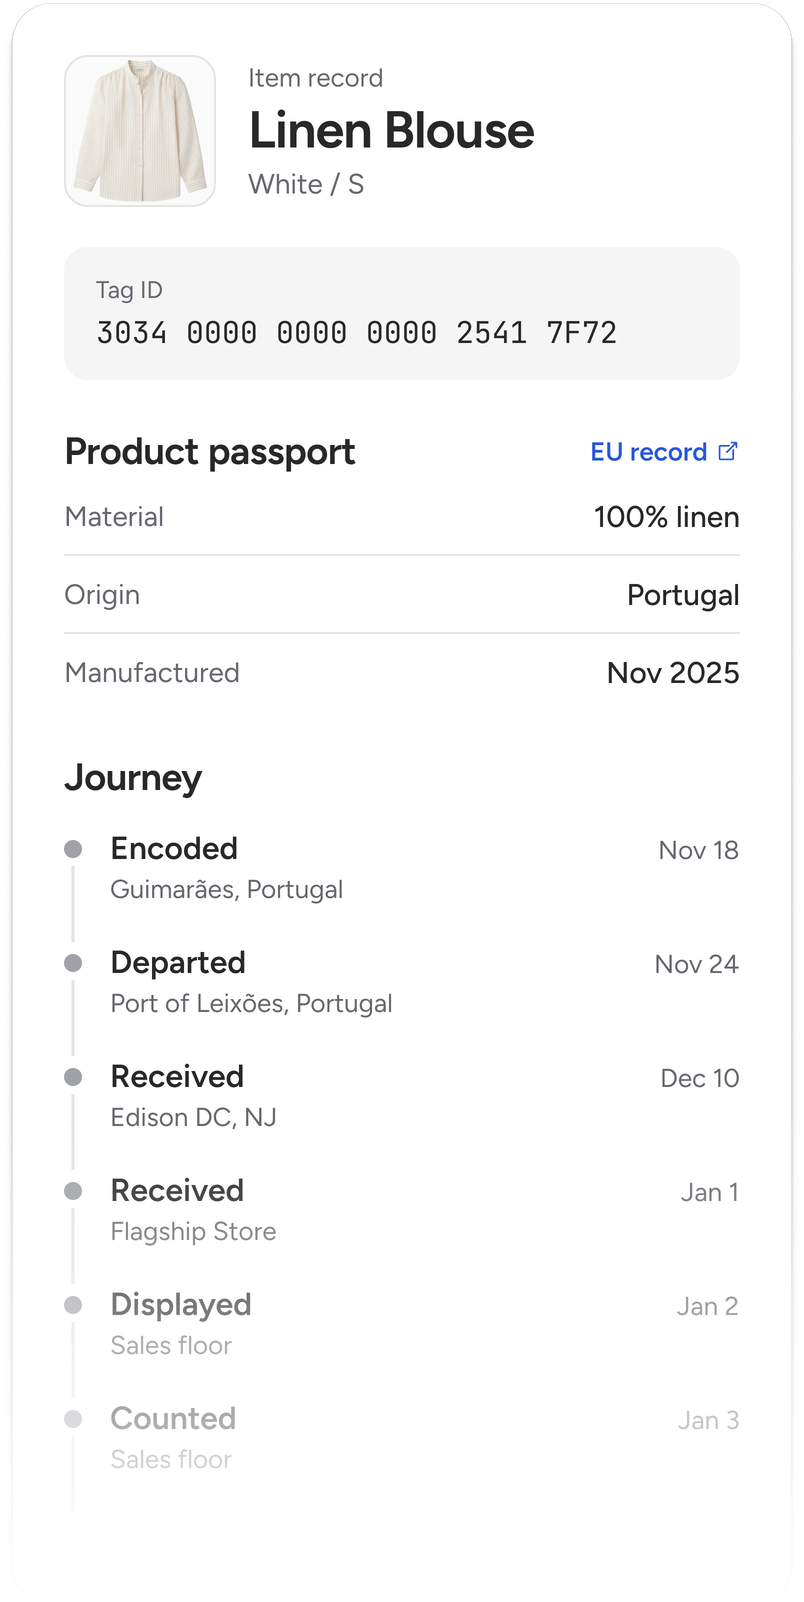
The Digital Product Passport arrives in 2027.
EU rules will require textile products to carry a digital record of what they are and where they came from. Item-level identity is the foundation that requirement sits on, which puts retailers already running RFID in a considerably better position than those starting from a barcode.
We are building toward it now rather than treating it as a 2027 problem, because the retailers that will find it easiest are the ones already tagging at item level today.
Security review does not have to wait for a contract.
Security review is the step most likely to delay a rollout, and the one most easily run alongside everything else. All of it is available before anything is signed.
Control documentation
The current documentation across all three frameworks, available for your team to review before a pilot begins rather than after a contract is drafted.
Architecture review
A working session with the people who built it, covering data flows, hosting, retention, and where your data physically sits.
Questionnaires
We complete vendor security questionnaires as a matter of course. Send yours with the scoping request and it runs alongside rather than afterwards.
Pilot-stage review
A free POC handles real data, so the security conversation happens before it starts. That is deliberate, and it is the best time to have it.
Send the questionnaire.
Your security team will get straight answers about what is certified, what is under audit, and what is planned, with dates rather than adjectives.